We’ve been busy but quiet these last months.
@npub1qw6s...4882 improved the site a lot by adding new features around #nostr based build verifications.
We hope other projects in the nostr ecosystem like
@franzap @Zapstore will see the value of these verifications and start integrating them. The more products that build on reproducibility, the more users can truly apply the principle of “Don’t trust - verify.” Binary transparency shouldn’t remain a niche feature - it needs to become the default.
If you run software that touches your private keys - be it nostr clients or bitcoin wallets - without binary transparency, only whoever built the binary really knows what code you’re running.
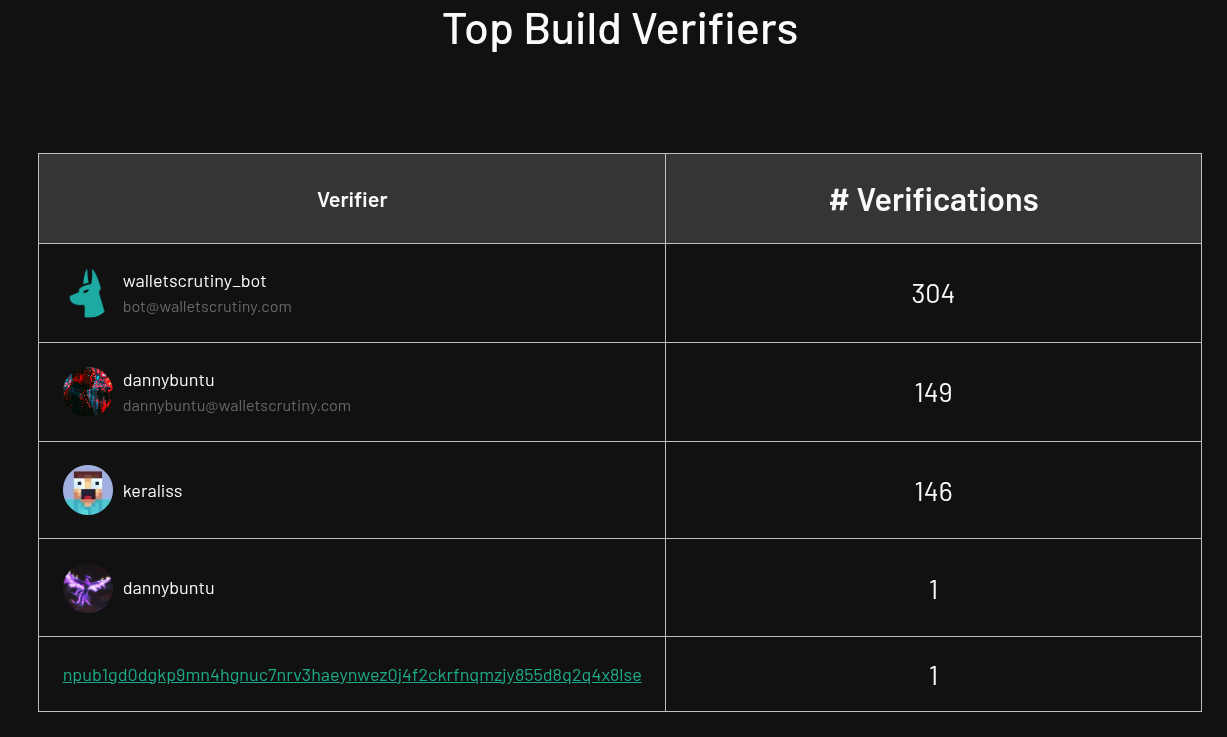 @npub1r709...sf7d
and
@keraliss checked the reproducibility of almost 300 binaries. The 304 verifications by
@npub1z69h...aukf are all the old verifications we had migrated to nostr. And the backlog keeps growing as we cover more and more products with frequent updates.
Are we doing something valuable for the space? A
@Spiral grant says yes, and community endorsements confirm it - but the project itself also needs scrutiny.
We recently introduced "verification endorsements":
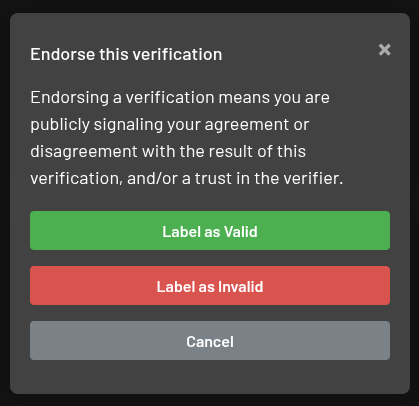
This is a simple contribution many could provide. If you read a verification and it looked plausible and complete and you trust the author, mark the verification as verified. If you ran the documented commands yourself on your hardware and got to similar results, please endorse the verification!
Even more importantly label verifications as invalid and leave a comment about what's missing when you find issues! Don't be shy!
Our goal is to document all steps such that all mildly technical users (you should be comfortable with a Linux shell) can reproduce our findings. If that's not the case, please provide your feedback and we will improve ✋.
And if you maintain one of the products we check, share your own verification as a template for others!

 WalletScrutiny turned 6!
We've come a long way over the years. In the beginning, we only looked into Android wallets - 40 of them - and now we've grown to more than 6000 products across many platforms. Your favorite hardware wallet? We got you covered. Desktop? Probably, too. And desktop is a lot of work as here we found many open source and reproducible products!