Replies (10)

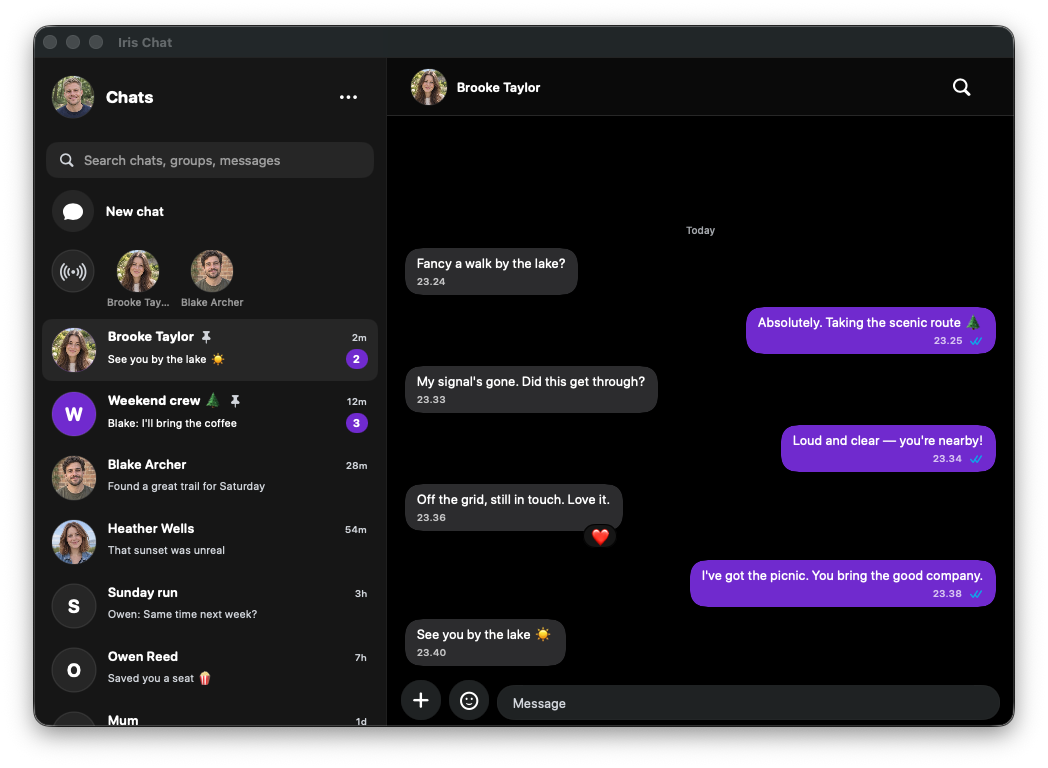
Probably really cool, but chat is so fragmented over nostr - what's this compatible or incompatible with that's already out there?
@Zapstore maybe it is worth tagging apps as "perceived spoofs" so users can be protected by WoT? I don't know where to draw the line between "remove it and/or ban/block the author" and "let the community protect themselves" I don't think every Zapstore user will have a WoT they can trust. Many will probably start with none.
Which one is a spoof exactly? I don't think anyone has a monopoly on the word Iris. It's a hard problem and we're tackling it in v2, actually, basing reputation on nostr was a mistake
Very nice! Keep in mind, building a safe and working IM is a very hard task. There are whole companies and multiple teams dedicated to do that and it is still problematic for them. If I could build an IM right now, I would not attempt it. What I always point at is the received data sanitization and safe local storage deletion. There are two types of threats: - received data - unexpected client behavior - stored data having the ability to kill the user if not deleted properly (from the storage and the network) Both are really dangerous. One can cause leaks/hacks/infection, the other, even worse things Try to virtually put yourself in a position of a person whos phone is about to be infected by a bug in an image handling library or for example a markdown library - how would you prevent it If the underlying nand can be read, and old messages extracted - how to prevent it If an attacker did get access to the device for a brief moment, can he silently clone the account and receive all the communication in the real time in his own environment without the user noticing And 31337 other important questions. Some solutions can be just copied from existing IMs So yeah, IMs are a big deal! Good luck!
Vast minority of apps are nostr signed, so nostr can't be the center of reputation. Certificates are, and they get reputation from multiple sources including nostr. Even with some trust in the catalog this is actually more useful. Also, no more certificate mismatch errors.
↑