GM Dear Nostr,
I need your help. I need all the arguments you can think of, why it would be a terrible idea to build public infrastructure based on ActvityPub and/or atproto instead of Nostr.
There is a public recommendation for action for german education infrastructure that says that open protocol based initiatives should be used in near future to get rid of big tech companies in public education infrastructures. But they name EuroSky and Fediverse as examples.
I need to get Nostr in there for reasons. So I would like to collect the biggest list of counter arguments. Technical, sustainability, societal perspectives, whatever comes to your mind.
cc @Constant @Sebastix @Jurjen de Vries @Sync @verbiricha @Renaud Lifchitz you got much bigger reach, please share π«
#asknostr
Login to reply
Replies (24)
wow what an argument.
I'm paying taxes if I like it or not. I would like to see them spent on sensible stuff and not going to waste
Gm! I will think about that later!
## Identity
ActivityPub identities are constitutively bound to a domain: @user@instance.state.de. The domain is not an address but part of the identity itself. In a federal system where each state runs its own instance, identity is therefore state-bound β and it ends when the state stops operating. Mastodon's Move migrates followers but not content, and requires the origin instance to still be running and cooperating.
The more serious issue is reference integrity. If state A cites resources from state B in collections, curriculum mappings or learning paths, and B shuts down its instance, it is not only accounts that break but every reference to them. In an infrastructure built for cross-state reuse, that is a structural defect rather than an operational risk.
In Nostr the key is the identity. Domains still appear via NIP-05, but as a revocable, replaceable attribute rather than a foundation. A state can shut down its relay without breaking a single identity or reference; the events remain verifiable on any other relay. Responsibility for operations is thus decoupled from responsibility for identity β a far better fit for federal reality than a model in which one state's exit devalues everyone else's data.
## atproto: portability (but with a directory caveat)
The AT Protocol addresses this. Identity there is a DID, not a domain; the handle is merely an alias proven via DNS or HTTP and can be changed without breaking the identity. Migrating between Personal Data Servers is supported, and repositories can be exported and re-imported elsewhere. Rotation keys even let an identity survive loss of the signing key β but only because in normal operation the PDS operator holds such a key in trust. Recoverability is solved organisationally, not cryptographically: whoever can rescue the identity can also alter it. The tie to an operator is loosened, not removed.
The second caveat concerns resolution itself. `did:plc`, the method used almost exclusively in practice, is not a self-certifying identifier but points to a central directory, so far operated by Bluesky PBC. It is auditable, but its failure interrupts identity resolution network-wide, and its operator can change without the federation having any say. For public education infrastructure planned in decades, this merely relocates the dependency: from a state domain to a commercially operated registry in another jurisdiction. The alternative, `did:web`, avoids that but reintroduces exactly the domain binding we set out to escape.
## The Eurosky case
The obvious rejoinder is that sovereign European atproto infrastructure already exists. Eurosky (https://eurosky.tech/), a project of the Dutch Stichting Modal, runs its own Personal Data Server: data sits in Hetzner facilities in Falkenstein, Eurosky operates the service itself, the contract is held by the foundation, and the service falls under European law including GDPR and DSA. That is substantial and relevant for public bodies.
But it concerns the hosting layer, which was never the problem: that anyone may run a PDS is an explicit design feature and permissionless by intent. **The identity layer is untouched: a Eurosky account still carries a did:plc identity resolved against the same central directory**. Data held in Germany, identity resolved through a registry in foreign hands β for an argument resting on digital sovereignty, that is a solution at one layer, not throughout. The rotation-key trust relationship likewise only shifts, from Bluesky PBC to a Dutch foundation: still operator-mediated.
There is also the protocol's practical shape. atproto is built around a few large aggregators processing the whole network's traffic; as of early 2026, Bluesky PBC still ran the only full-network AppView. That suits a platform, less so a landscape of sixteen states, media centres and other bodies each running small nodes and exchanging selectively.
## Key loss
The obvious objection to key-based identity: what happens when a key is lost, and who is responsible in an administrative context? It must be addressed, but it is solvable.
For individual users, FROSTR and pomegranate offer approaches based on FROST signatures, standardised as RFC 9591: the key is split into shares, and signing requires k of n.
The contrast with the atproto model is therefore precise: there, one party must be able to act alone for recovery to work at all. Here, participation is possible without sole authority.
## Signatures
Nostr events are atomic and self-verifiable: generate a hash, verify the Schnorr signature against the public keyβoffline, without network access, and without additional context. The key *is* the identity.
In atproto, the signature is attached to the repository commit rather than the individual record. While individual verification is possible, it requires an inclusion proof via the PLC directory. Consequently, verification is no longer self-contained; it has a runtime dependency on a central entity.
In standard operation, ActivityPub signs the delivery process using the server key, not the object itself. Once forwarded, the content cannot be independently verified; object-bound signatures exist only as an optional extension (FEP-8b32) with no widespread implementation.
For a distributed public infrastructure involving many small, heterogeneous consumers, the Nostr approach therefore offers a significantly lower barrier to entry: the artifact and the proof travel together, and any participant can verify the authenticity of a data record with just a few lines of code without needing to trust a relay, server, or directory.
See here:
View quoted note β
You don't want the German govt on here snooping about and legislating. They have the time, money and desire to send C&D letters to every relay operator and media host that doesn't follow whatever rules they decide to impose
I think the shit that was going on here with capgemini and billions lost in trying to build that monolith actually made *some* people loose trust in that consulting moneygrabbers.
But things just work in that way that they will have to fund activitypub / atproto stuff, if they find no arguments for nostr somewhere else. that's why we went to fosdem and hand in proposals at that luxembourg thing or not?
"show and tell": I attended every possible conference I could and dropped the word. I built for showing them that the solutions they are looking for are already there. A friend of mine is a prof for special education and is going right now from state to state to convince people of actually your example, because he got that nostr will actually enable this.
And some listened, but without lobbies like ones that
can run, it's hard for them to argue funding and exploring nostr based solutions further, because they will get asked why the fund stuff that's not recommended by that expert comissions. It's damn stupid, but that's how that shit works. I just want to make sure the money gets spent on something sensible. I already paid the last big failure they tried.

Eurosky
Eurosky β The social internet, rebuilt in Europe
Eurosky is a European initiative to build and operate sovereign social web infrastructure
Because they want to provide services where e.g. teachers can exchange ideas and learning content they develop, but where should they do it?
They can't say use WhatsApp or Insta, if they want to facilitate that as a general policy or want to support them, they need a service to do so.
And the only proocol coming to their mind that is already quite tested is activityPub to build upon. But I think it would be a huge mistake to do so, because of all the flaws, especially regarding identity that activityPub carries.
Simplicity. That ATproto is unbearably complex to implement and maintain
Plesse Start and solve it π
A I s l o p
My priority is this: if we start now developing public infra on ActivityPub in a federal system like Germany we end up like, ok every state runs its own activitypub instance. Then one state will drop out in the future, because they get a government that says I don't like whatever the previous government has done and will end this service and stop it.
The users will end up lost. Because they loose their public identity because it is domain based. All the references to content they produced might get lost.
That's why I think *any* domain based system is not suited for public infrastructure
What arguments do you disagree on?
Will reply later and will also get through the comments.
But for now
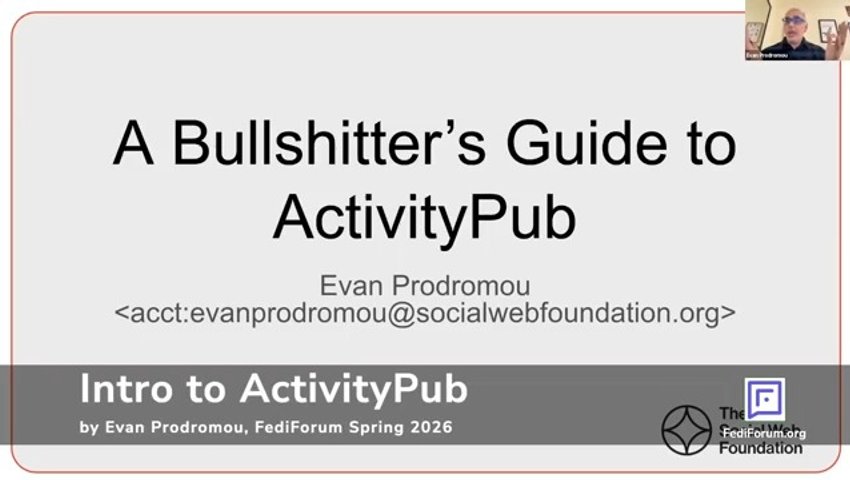
- this fediforum keynote can help you the current fediverse status
and perhaps also
(which I havent watched yet)
-
a 101 by @Alex Gleason (did he already shared his knowledge) and @MK Fain
-
resource by @Rabble
And also this fellow has done some things in the atmosphere
and is here in the nostrverse (I dont remember his handle now)
Spectra Video
FediForum Talk: How To Bullshit Your Way Through a Conversation about ActivityPub
By Evan Prodromou, Social Web Foundation and editor of the ActivityPub standard. One of the best bluffers in the field of distributed social networ...
Spectra Video
FediForum Talk: Atproto: A Technical Introduction
By Daniel Holmgren, head of protocol at Bluesky PBC. AT Protocol (atproto) is the open protocol powering Bluesky and the emerging Atmosphere. This...

Soapbox
Nostr vs. Fediverse vs. Bluesky: A Comparison of Decentralized Social Protocols - Soapbox Blog
While all three protocols aim to decentralize social media, they differ in their approach to decentralization, user identity control, and censorshi...

Declaration of Social Media Rights
Five fundamental rights we need for a free, open, and humane social media ecosystem

Gist
why-i-left-atproto.md
GitHub Gist: instantly share code, notes, and snippets.
Fix Nostr make no mistakes ! π«
If they're trying to get away from American infrastructure, the best argument would likely be that the Mastodon Inc (nonprofit) and Bluesky PBC are both registered in the United States.
On the technical side, Nostr:
* Has permanently referencable events and redundancy, meaning content can be archived and accessible beyond what AT/AP can do.
* Is a lot more flexible as a protocol. AFAIK you can't do ebooks and geocaching on anything other than Nostr
* Scaling a Nostr service is a lot easier and less resource intensive than scaling a large Activity Pub or AT based service
* Doesn't rely on DNS (heavily American influenced) or a centralized servers for identity management
Technical Drawbacks:
* Key based identities would need to be abstracted for the average user. Good luck having them manage their own keys.
Culture wise:
* Nostr also lacks some of the extremists that have congregated on ActivityPub (both left and right) and AT (left). Sure the BTC people can get a bit loud sometimes, but it's nothing compared to the dark corners of the other two protocols.
Finally, while it'd likely be considered a drawback to the German government, it'd be a benifit to the people that Nostr is decentralized enough that they can't rule it with an iron fist like they're likely eyeing with big centralized AT/AP services.
None, AI writing just makes me want to throw up
The key based argument is the one I get most confronted with, especially talking with devs of running services in that area. I guess we can mitigate this using trusted third party services as they already do. They continue using their identity providers, but its like using pomegenerate. But it will become much easier for people to communicate across services, move and reduce vendor lock in options.
Will recommend that π«‘ π€π€
Alright π«‘
Pls use as little tokens as possible tnk u
Thank you for this article on that perspective!
#2
1. A significant loss for a winemaker π₯
View quoted note β
2. A nostrich asks for help from the Nostr community ππ»
View quoted note β
3. It is worth checking this out π
View quoted note β
4. These kinds of incidents are so disappointing to the user ππ»
View quoted note β
5. Starting the day with this kind of Nostr note is so awesome β
View quoted note β
6. A huge release from Roadstr ππ»
View quoted note β
7. Submissions have closed. Time to judge & reward π
View quoted note β
8. A Nostrich enjoyed his 34th birthday with his heritance π
View quoted note β
9. We need these kinds of inspirations for the growth of Nostr ππ»
View quoted note β
10. Nostr creator suggests a solution to fix reply spam ππ»
View quoted note β
#community_nostr_recap
1. A significant loss for a winemaker π₯
View quoted note β
2. A nostrich asks for help from the Nostr community ππ»
View quoted note β
3. It is worth checking this out π
View quoted note β
4. These kinds of incidents are so disappointing to the user ππ»
View quoted note β
5. Starting the day with this kind of Nostr note is so awesome β
View quoted note β
6. A huge release from Roadstr ππ»
View quoted note β
7. Submissions have closed. Time to judge & reward π
View quoted note β
8. A Nostrich enjoyed his 34th birthday with his heritance π
View quoted note β
9. We need these kinds of inspirations for the growth of Nostr ππ»
View quoted note β
10. Nostr creator suggests a solution to fix reply spam ππ»
View quoted note β
#community_nostr_recap